Guide
All articles tagged Guide.
Practices that set great software architects apart
Great software architects don’t just make technical decisions—they balance competing priorities, navigate messy org charts, and align engineering with business strategy. This post explores the habits and mindset that separate competent architects from truly impactful ones, and why those differences matter. Whether you're eyeing the role or already in it, these are the practices that move the needle.

Cloud native chronicles: Lessons learned from building Cerbos in the open
What does it actually mean in practice to be Cloud Native? Having spent the last 2 years building the open source authorization layer Cerbos, we will cover the key software ingredients that contribute to a successful cloud-native project. Hear some of the hard-learned lessons, and the most sought-after aspects when venturing into your own cloud-native endeavours.

Revolutionize your authorization with Cerbos: A comprehensive video demo | ByteGrad
Discover how Cerbos simplifies authorization for microservices and Next.js applications in this video. Dive deep into Cerbos Hub's capabilities with a practical demo, showcasing ease of management and deployment. Watch now to enhance your security strategy.

Insights from KubeCon Europe 2025 - AI gets real, and identity gets serious
KubeCon Europe 2025 revealed a shift from AI hype to real-world operations, spotlighting the rise of identity-first architecture and policy-based access control. From secure workload identities to operationalizing AI, the cloud-native community is embracing maturity with scalable, secure infrastructure.
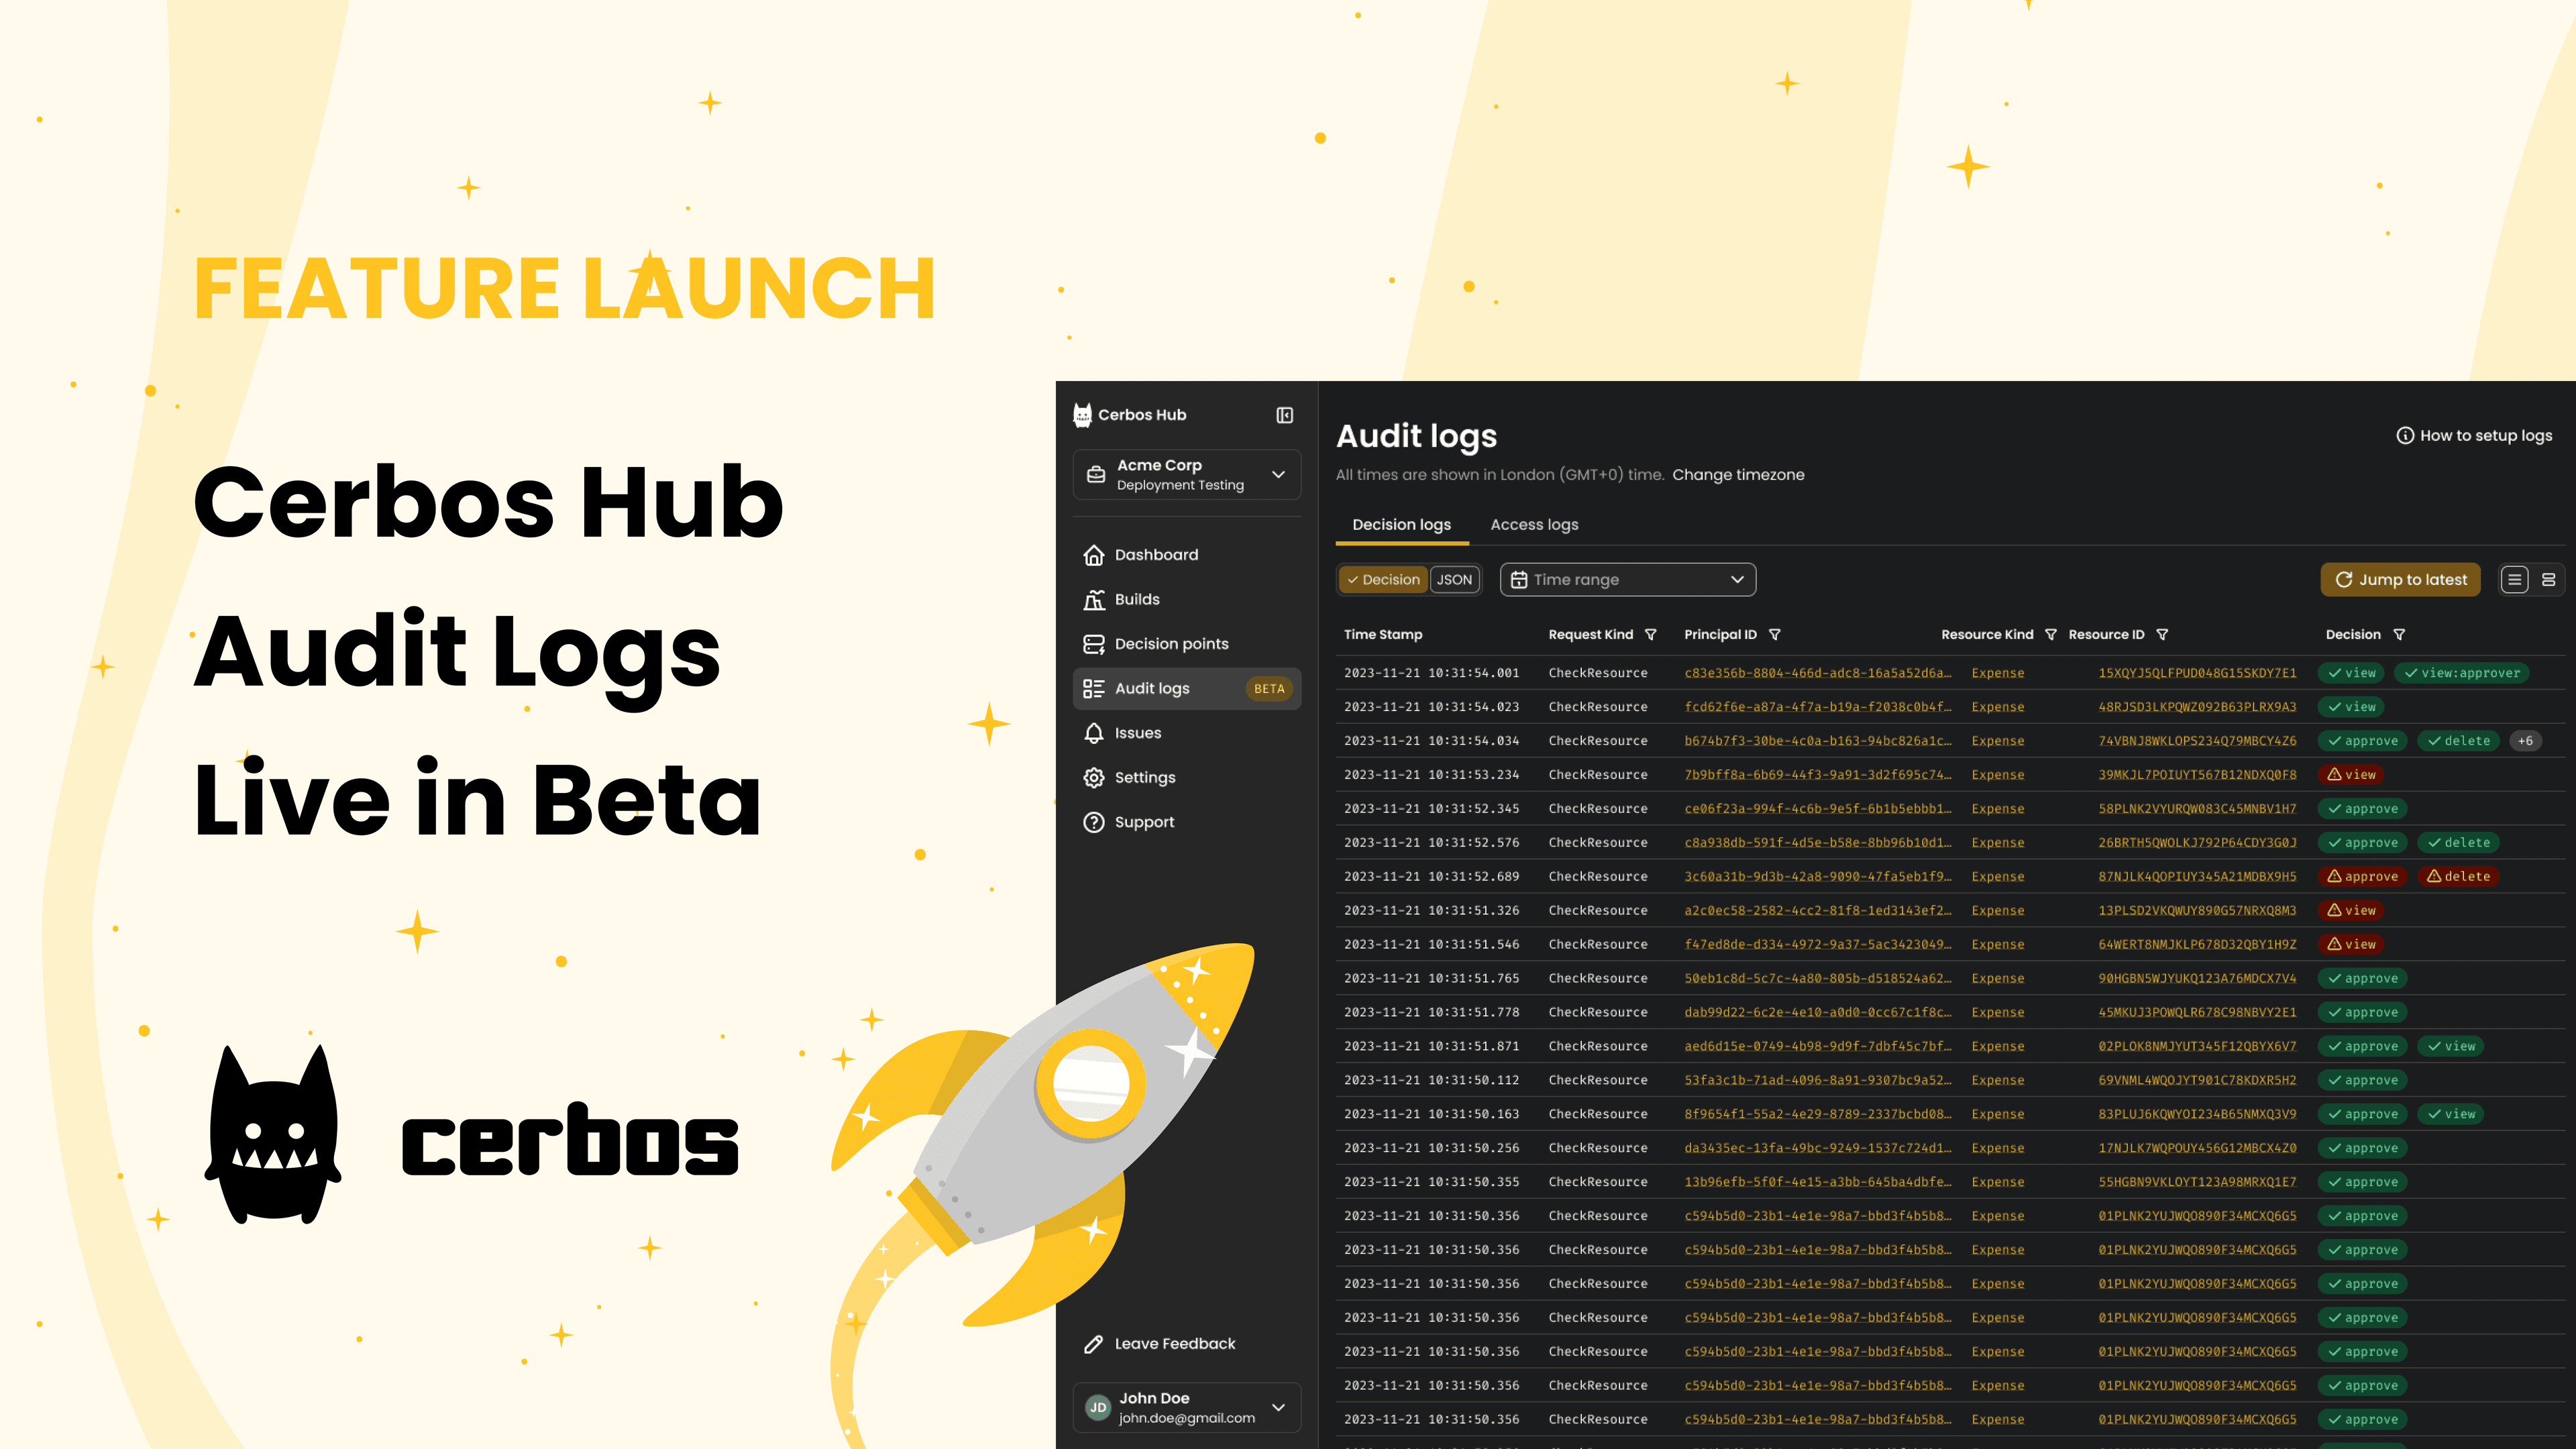
Cerbos Hub Audit Logs Live in Beta
Explore Cerbos Hub Audit Logs, now in beta! Capture detailed access and decision records across your PDPs, enabling faster debugging, enhanced security, and compliance verification. Ideal for developers, security engineers, and product managers, this feature streamlines your workflow and provides deep insights into authorization decisions.

Recap of webinar: "Simplify access controls in Node.js, React & serverless apps" | Cerbos & ByteGrad
Join Alex Olivier, Cerbos Chief Product Officer, and Wesley, presenter of the popular ByteGrad Youtube channel, as they demonstrate how to author permissions and policy changes using Cerbos, and deploy those changes without changing any other code.
From OPA to our own engine - the Cerbos journey
When we started building Cerbos in January of 2021, we had a clear mission. We wanted to help developers separate their roles and permissions management from the core application code, creating a more scalable and future-proof way of handling permissions. This is the story of how we began with Open Policy Agent (OPA) and eventually built our own policy decision engine, and why that transition was crucial for our product's evolution.

What is admin-time / static authorization?
This article will explain what admin time authorization is, why it matters for software architects and developers, and how it contrasts with dynamic, run-time checks. We’ll also touch on real-world scenarios to illustrate the concept, and briefly discuss how newer solutions tie these models together for better security and compliance.
Implementing an authorization model for a SaaS application
SaaS applications require robust authorization models, although selecting the right approach for your system can be daunting. This article outlines a solid method for implementing authorization within a typical workspace SaaS application.

What is data authorization?
Data authorization provides fine-grained access control. Understand why data authorization matters, and how organizations can implement it to reduce risk, meet compliance requirements, and enhance user experience.

How Cerbos works
Discover how Cerbos can integrate seamlessly into your existing software ecosystem. In this blog post, we go through Cerbos' functionality, main features, and the benefits of using Cerbos for fine-grained authorization in your applications.

Embracing WebAssembly in authorization | Cerbos, KubeCon + CloudNativeCon Paris
The intersection of Kubernetes, cloud-native solutions, and WebAssembly (WASM) represents a frontier of innovation. At the recent KubeCon EU conference, Alex Olivier, CPO and Co-Founder of Cerbos, shared insights during an interview with Milo Oudenaller from Amazic.
Access control and permission management for AI agents: building with security in mind
AI-powered chatbots and agents are value-adding features for many companies, helping both company employees and external users, who interact with the company products. The key challenge here is that these chatbots should provide contextually useful responses that would solve users' problems without leaking sensitive information. Read on to see how this can be achieved.
Role-based access control best practices: 11 top tips
Role-Based Access Control is an access control model based on clearly defined roles. Read on to learn more about Role-Based Access Control best practices.

Cerbos Playground: Dive into the RBAC policy generator
Access control in modern applications is crucial to ensure data privacy and system integrity. As applications become more complex and interconnected, so does the need for a more simplified way to manage access controls. This piece showcases Cerbos Playground's newest feature - the RBAC Policy Generator.

Cerbos Dagger module for authorization testing
Introducing the Cerbos Dagger module: a tool to streamline authorization testing by externalizing policies, integrating with CI pipelines, and simplifying permission management. Learn how this module can enhance your application's security and maintainability. Watch the demo and explore more on GitHub.
Understanding security and access control requirements of microservices environment
Learn how you can implement robust security protocols and access control measures to ensure inter-services communicating is not compromised.

Authorization in developer workflows: best practices and tools
Authorization can be a powerful enabler of developer creativity and seamless user experiences—but only when treated as a first-class workflow concern. Explore how modern authorization patterns can improve security, productivity, and the developer experience itself!