Guide
All articles tagged Guide.
Gartner IAM Summit 2025: Authorization maturity, AuthZEN momentum, and why identity security is expanding to every workload
Gartner IAM Summit 2025 insights on authorization maturity, Workload IAM, and AuthZEN. Learn why policy based, externalized authorization is becoming core identity infrastructure for modern workloads and AI agents.

Secure RAG: Implement LLM Access Control with Cerbos
Learn how to implement access control for RAG and LLMs. Maintain data security and compliance with fine-grained authorization for your RAG and LLMs. Enforce your organization’s permissions within your AI system.
Key compliance regulations for non-human identities
A clear guide to key compliance regulations for non-human identities across PCI DSS, DORA, NIS2, ISO 27001, HIPAA, GDPR, and SOC 2. Plus what auditors expect and how to prepare.
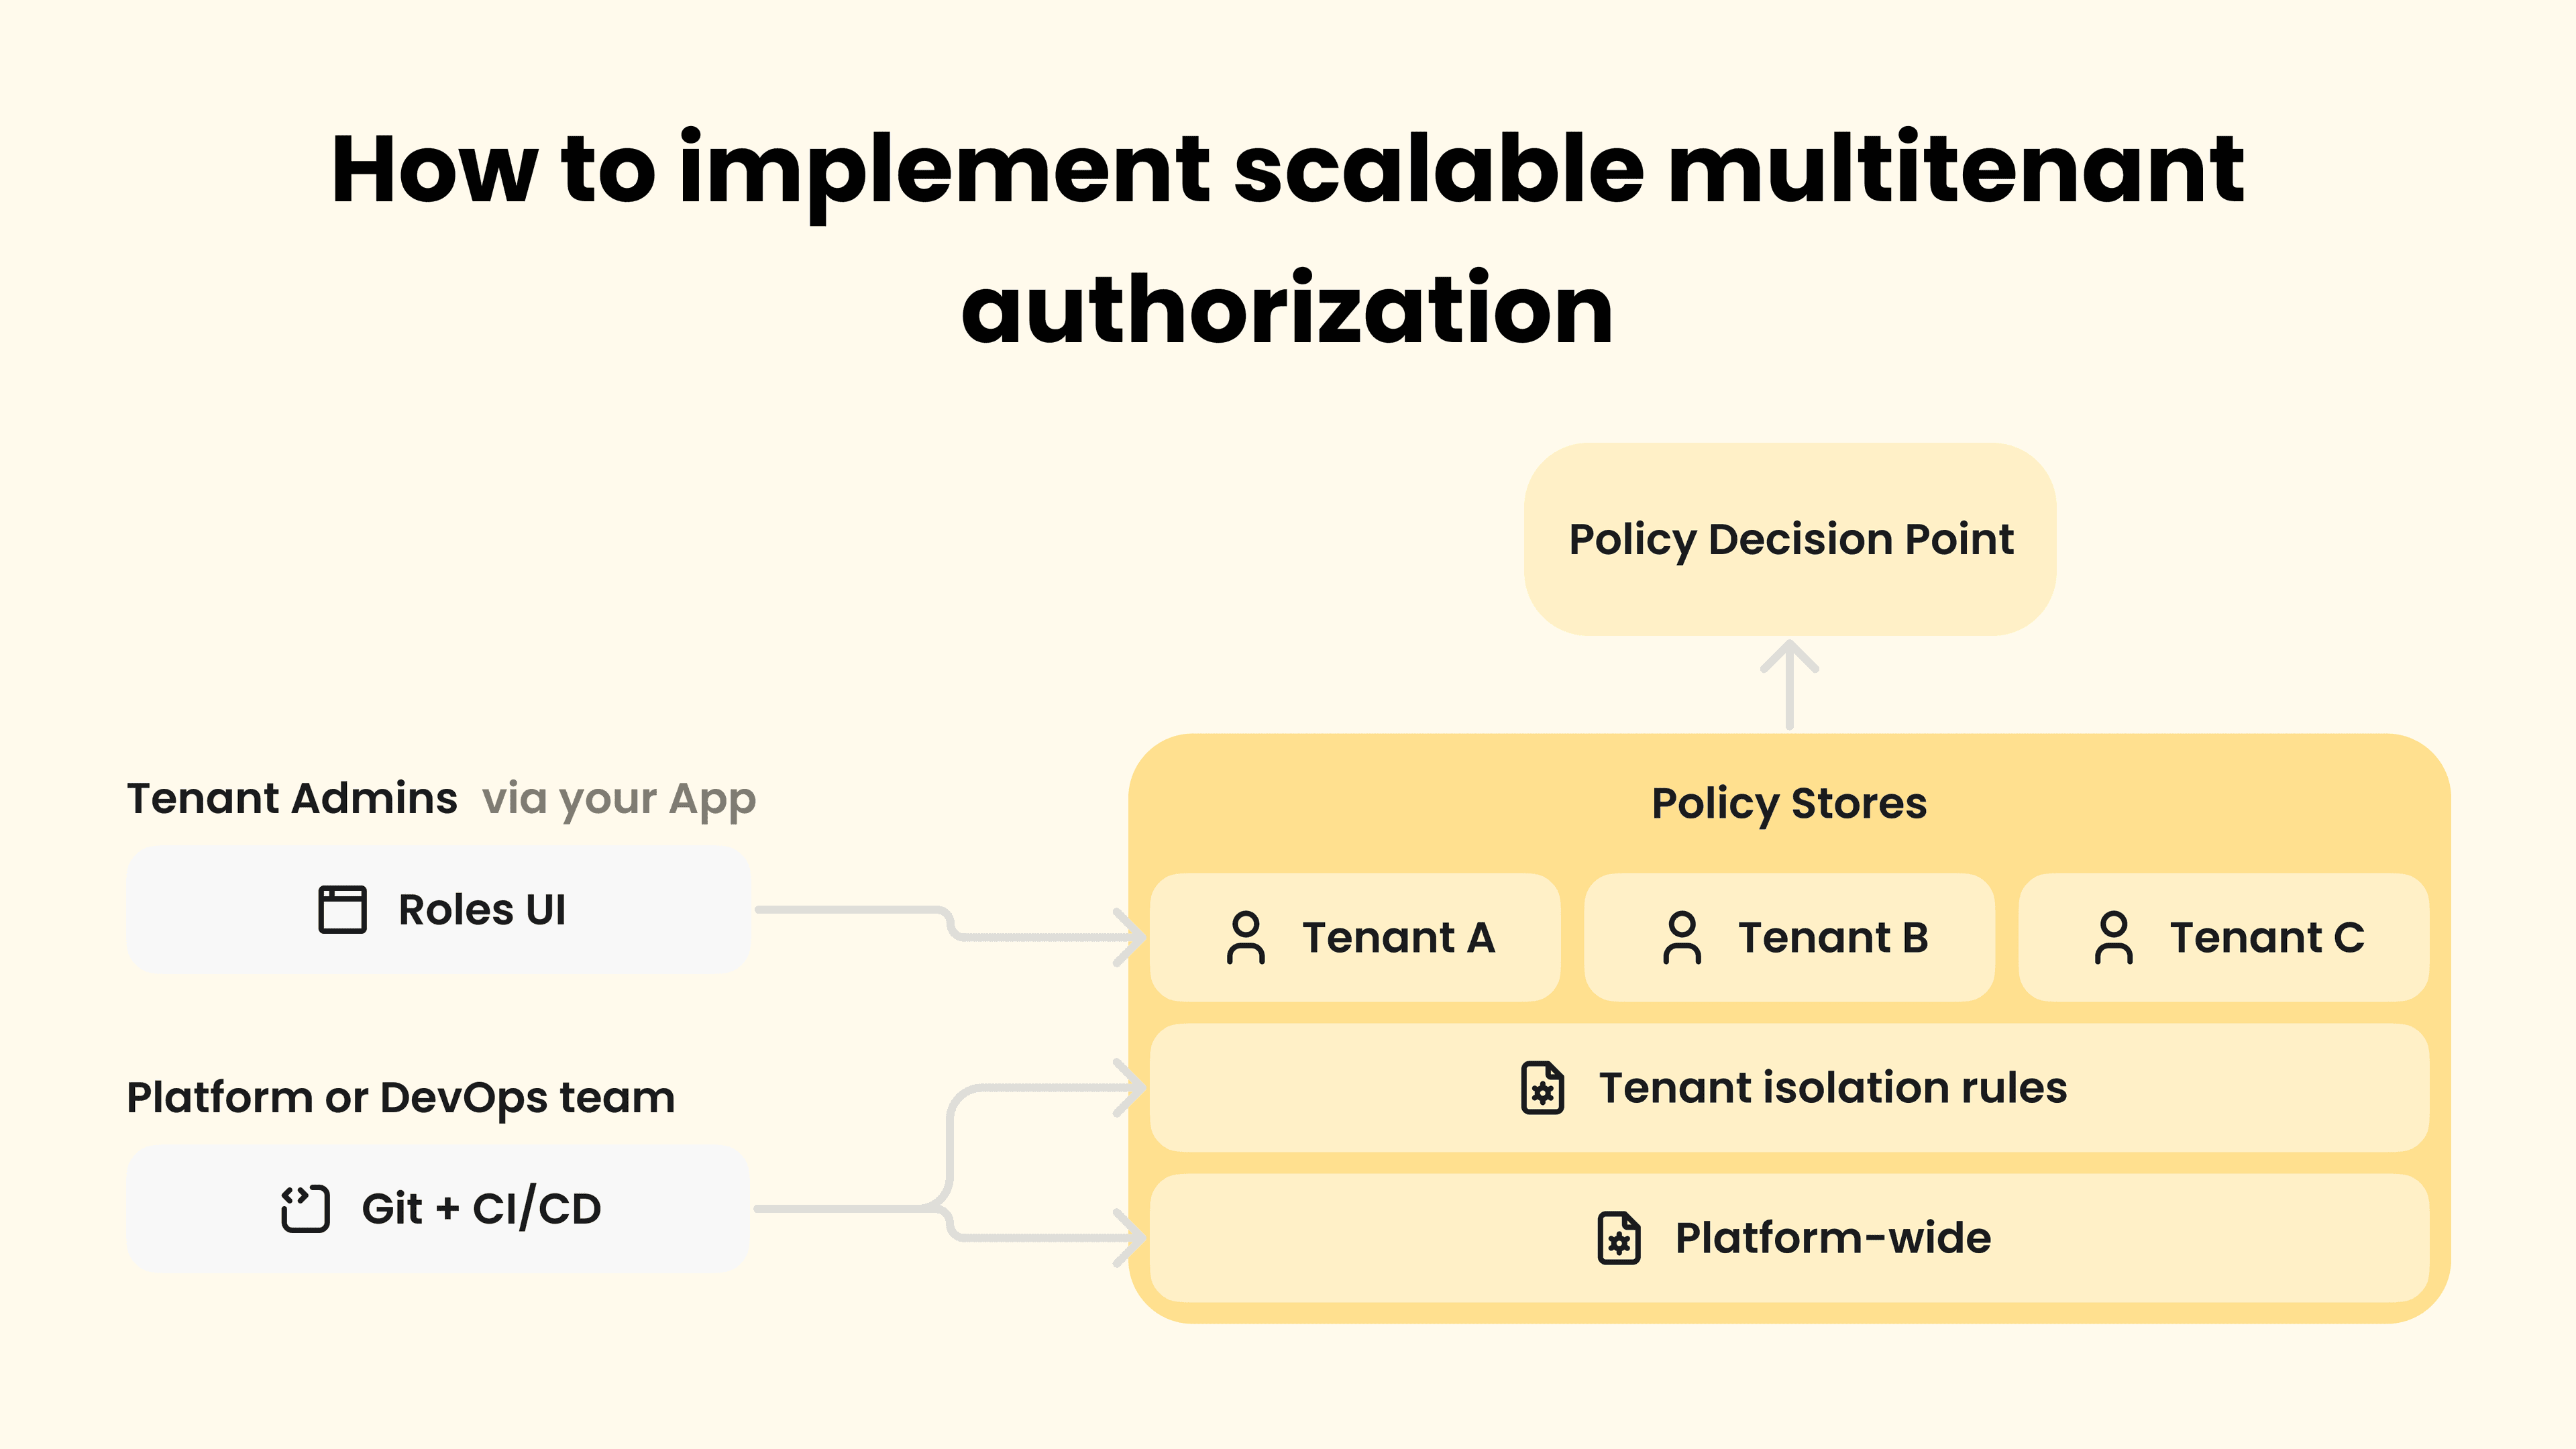
How to implement scalable multitenant authorization
Implement multitenant authorization without role explosion. Learn how tenant-aware roles, ABAC, and externalized policy engines provide secure, flexible, and maintainable access control for multitenant applications.

Cerbos vs. OPA
Understand the differences between Cerbos and OPA across policy language, developer experience, architecture, performance, and policy management. We will also show the strengths and limitations of each solution and discuss practical trade-offs.
Key takeaways from Workload Identity Day 0 at KubeCon
Workload Identity Day 0 revealed SPIFFE’s dominance and exposed rising risks in non-human and AI-driven identities. Learn why modern workloads demand strong identity, fine-grained authorization, and platform-level security to stay compliant and resilient as AI agents scale.

What is Cerbos?
What Cerbos is, and why it should be the go to for authorization.

Mongoose adapter for Cerbos Query Plans v2.0
Speed up authorization in MongoDB with Cerbos Query Plans and the enhanced Mongoose adapter. Enforce policy logic in-database and return only allowed records.

Staying compliant - What you need to know
Staying on top of compliance has become essential for businesses today. In this article we examine the key elements of compliance that should be prioritized, from data quality and change management to audit logs and access control. We also explore how picking the right authorization system can strengthen your compliance efforts.
Migrating from OPA and Rego to Cerbos
Learn how to migrate from from OPA and Rego to Cerbos. This guide walks you through the differences, how to translate common patterns, how to update your integration layer, and how to roll out the migration safely.
Broken access control still tops the list: OWASP top 10 2025
Learn why Broken Access Control remains the top OWASP 2025 risk and how Cerbos provides scalable, fine-grained authorization to prevent object-level and contextual access failures.
Platform engineering leaders are racing to enable AI safely - takeaways from KubeCon NA 2025
Discover how platform engineering leaders at KubeCon NA use a three-lane model, sandboxes, and shift-down security to accelerate safe AI adoption, govern AI agents, and protect developer velocity.
AuthZEN: Standards-based authorization for enterprises
Authorization used to lack the standards authentication gained with OAuth and OpenID. AuthZEN, backed by the OpenID Foundation, introduces a unified model for externalized, fine-grained, and interoperable access control. Discover how Cerbos supports AuthZEN to deliver modern, standardized enterprise authorization.
What ISC2 congress 2025 made clear about modern compliance
ISC2 Congress 2025 highlighted the shift from policy documentation to policy as code. Learn how security leaders are implementing continuous compliance, governing AI systems, quantifying cyber risk, and embedding enforcement directly into infrastructure for measurable, auditable security controls.
Mapping business requirements to authorization policy in HR systems
Best practices for translating business requirements into authorization policy for your Human Resources (HR) system. We walk through the process of reviewing business requirements, analyzing them, defining policies, and ultimately deploying them to production systems as efficiently as possible.
Mapping business requirements to authorization policy for insurance
Explore how insurance companies can combat fraud with modern authorization. This guide explains PBAC in action across auto, life, and property insurance; with practical examples and policy templates to help you implement secure, fraud-resistant access control in your organization.
Run Cerbos natively inside AWS Lambda
Deploy Cerbos directly in AWS Lambda-either as a standalone function or as a lightweight extension layer-while using Cerbos Hub for centralized policy management and audit-logging.

Building your own authorization solution vs. buying an off-the-shelf one
Build vs. buy for authorization. There is no standard answer to the perennial build vs. buy question, but the argument for rolling your own authorization is getting harder to make. In this article, we help you speedrun the build vs. buy decision by breaking down your choices, so you can evaluate what’s best for your situation.