Cerbos Synapse
Give every authorization decision the context it needs
Assemble identity, resource, and relationship context from your IdPs, databases, and APIs, and connect enforcement points through the protocols they already use for consistent authorization decisions


Rob Crowe, Principal Engineer, Utility Warehouse
“We rely on Cerbos to make authorization decisions across the whole mesh - millions of times a day.”

Unified authorization context
Real-time context from your data fabric
Fetch identity, resource, relationship data at decision time for true zero-trust authorization, without custom middleware or PEP code.

One platform for authorization management
End-to-end authorization across applications, infrastructure, and AI systems with a unified policy engine, data layer, and control plane.
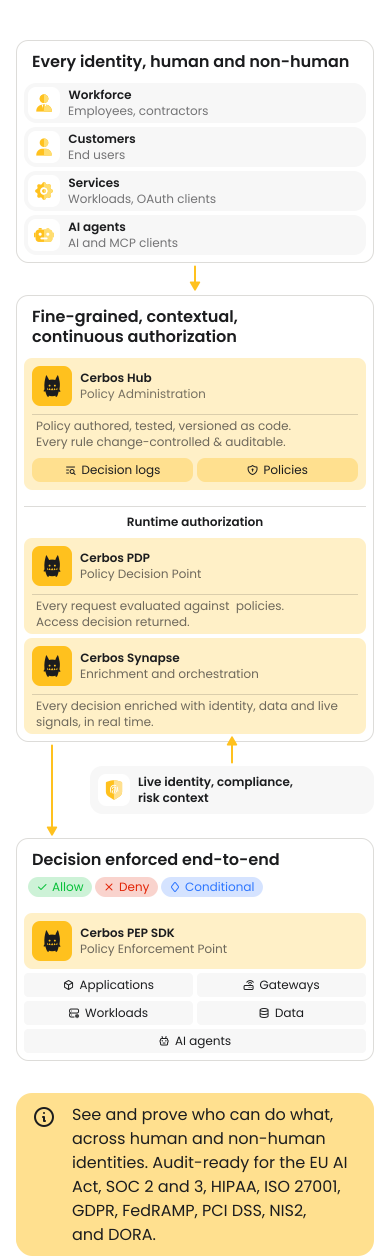
End-to-end authorization platform
Policy management, data enrichment, access decisions, and enforcement in one solution
Authorization management
Cerbos Hub
Policy Administration Point
Cerbos Hub is the control plane for policy authoring, testing, versioning, distribution, and audit visibility. Hub provides end-to-end policy management out of the box.
Data and integration
Cerbos Synapse
Enrichment and Orchestration
Synapse fetches identity, resource, and relationship data from external systems to enrich authorization requests, and translates infrastructure protocols into Cerbos policy checks.
< 1 ms decision time
Cerbos PDP
Policy Decision Point
PDP is an open source authorization engine that evaluates requests against policies and returns access decisions. It's stateless, high-performance, and built to scale horizontally.
Native SDKs
Cerbos PEP SDK
Policy Enforcement Point
Cerbos PEPs are language-native client libraries that connect applications directly to PDPs to enforce real-time access decisions, with SDKs available for all major languages.
Authorization across every system and use case
AI systems authorization


Enterprise software authorization


Authorization software that scales with your business
ABAC
RBAC
ReBAC
PBAC
Runtime
Event-time
Admin-time
Audit-time
Cloud
Self-hosted
On-premise
Air-gapped
Non-human identities
Human identities
Workloads
AI agents carry minimal identity context. Cerbos fills the gap.
When an agent acts on behalf of a user, Cerbos enriches the request with the user’s full identity, session, and resource context for fine-grained authorization decisions.

Identify the human behind every agent request
Synapse can fetch the delegating user's profile from your IdP and pass both identities to the policy engine in one call.
Evaluate agent and human together
One policy call evaluates what the agent is allowed to do and whether the user behind it is authorized to trigger that action.

No standing privilege for non-human identities
Access is never assumed from a previous decision. Every agent request is checked against the current policy at request time.
Let agents discover what's allowed
Query planning returns the full set of resources an agent can access on behalf of a user, with the same enrichment applied.

Full audit trail for every agent decision
Capture the enriched authorization request and decision outcome for full traceability across agent and human access decisions.


Developer-ready integrations
Works with your existing tools, workflows, and infrastructure

Identity provider enrichment
Fetch user profiles, groups, and attributes from Okta, Entra ID, Cognito, LDAP, and other identity providers.


Infrastructure integrations
Authorize access from API Gateways, messaging queues, data platforms, deployment pipelines, and other systems using the authorization protocols they support.



Data sources and databases
Retrieve identity and resource attributes from SQL databases, graph stores, and internal APIs.



Custom extensions
Build custom data sources, protocol adapters, and request transformations in any language that compiles to WebAssembly.


Implementing Zero Trust with Cerbos
Why engineering teams love Cerbos
"When I did an audit, I found that the cost of managing authorization and authentication in-house over the entire lifespan of the company was in the 7 figures. Cerbos saved that. Deploying Cerbos has allowed our engineers to spend their time on what really matters for our success."
Chuck Hardy
Head of Engineering @Salesroom
"Having to modify authorization is a five-minute job now. Having to troubleshoot authorization is a five-minute job. So that has actually allowed the team to spend more time where it really matters on the platform."
Karen Kim
CEO @Human Managed
"We rely on Cerbos to make authorization decisions across the whole mesh - millions of times a day. And it’s fast. We don’t even think about it anymore. It just works."

Rob Crowe
Principal Engineer @Utility Warehouse
"We went from one user - every role, to a world where there are many users - many roles. And the product, it relies on Cerbos to actually bring the value that we want to bring to customers. All of our customers are relying on Cerbos, by relying on the product, which is of course relying on Cerbos."
Joe Lines
CEO & Co-Founder @Nook
"One of our big considerations was speed. We have strict latency tolerances. When it comes to Cerbos - you can call it a hundred times during a request and it doesn't matter. It's incredibly fast."
Steve High
Staff Engineer @Complex
"The main reason we switched to Cerbos was to have a sophisticated authorization software to help organize and handle our authorization. We wanted to focus on domain related features and spend less time backtracking and fixing issues with our authorization."
Lead Software Developer at @BarrierSystems
"Cerbos enables us to go to market very quickly, compared to an in-house solution. It allows us to offer new products faster, because creating or editing policies is so easy."
Engin Attar
Head of Product and Growth, Co-Founder @Debite
"We got the foundation set. Now we can scale and include more complex policies. And we can grow in the right direction and with the right security thanks to Cerbos authorization management."
Edgar Rivera
CTO @4gcapital
"Having the separation of the permissions from the code base just makes the code base more elegant. It makes the permissioning more elegant. It means they're centralized, so they're not tied to specific endpoints. And ultimately it means that different business owners have the ability to actually make updates."
Henry Arnold
CTO & Co-Founder @Nook
"We're not worried about scaling because we can easily increase our load on Cerbos. It will also be easy for us to change how we're distributing policies as we reach different points of scale."
David Workman
Senior Software Engineer @ Salesroom

"Offering dynamic roles and permissions makes us more competitive in the market. We’re providing companies with a software that can be adapted to their workflows."
Ibrahim Bou Ncoula
CTO @Supy
"We can create unlimited conditions, attributes, and parameters at any level of granularity without writing any code. It allows us to deliver truly personalized services quickly, securely, and at scale."
Karen Kim
CEO @Human Managed
"When I did an audit, I found that the cost of managing authorization and authentication in-house over the entire lifespan of the company was in the 7 figures. Cerbos saved that. Deploying Cerbos has allowed our engineers to spend their time on what really matters for our success."
Chuck Hardy
Head of Engineering @Salesroom
"Having to modify authorization is a five-minute job now. Having to troubleshoot authorization is a five-minute job. So that has actually allowed the team to spend more time where it really matters on the platform."
Karen Kim
CEO @Human Managed
"We rely on Cerbos to make authorization decisions across the whole mesh - millions of times a day. And it’s fast. We don’t even think about it anymore. It just works."
Rob Crowe
Principal Engineer @Utility Warehouse
"We went from one user - every role, to a world where there are many users - many roles. And the product, it relies on Cerbos to actually bring the value that we want to bring to customers. All of our customers are relying on Cerbos, by relying on the product, which is of course relying on Cerbos."
Joe Lines
CEO & Co-Founder @Nook
"One of our big considerations was speed. We have strict latency tolerances. When it comes to Cerbos - you can call it a hundred times during a request and it doesn't matter. It's incredibly fast."
Steve High
Staff Engineer @Complex
"The main reason we switched to Cerbos was to have a sophisticated authorization software to help organize and handle our authorization. We wanted to focus on domain related features and spend less time backtracking and fixing issues with our authorization."
Lead Software Developer at @BarrierSystems
"Cerbos enables us to go to market very quickly, compared to an in-house solution. It allows us to offer new products faster, because creating or editing policies is so easy."
Engin Attar
Head of Product and Growth, Co-Founder @Debite
"We got the foundation set. Now we can scale and include more complex policies. And we can grow in the right direction and with the right security thanks to Cerbos authorization management."
Edgar Rivera
CTO @4gcapital
"Having the separation of the permissions from the code base just makes the code base more elegant. It makes the permissioning more elegant. It means they're centralized, so they're not tied to specific endpoints. And ultimately it means that different business owners have the ability to actually make updates."
Henry Arnold
CTO & Co-Founder @Nook
"We're not worried about scaling because we can easily increase our load on Cerbos. It will also be easy for us to change how we're distributing policies as we reach different points of scale."
David Workman
Senior Software Engineer @ Salesroom
"Offering dynamic roles and permissions makes us more competitive in the market. We’re providing companies with a software that can be adapted to their workflows."
Ibrahim Bou Ncoula
CTO @Supy
"We can create unlimited conditions, attributes, and parameters at any level of granularity without writing any code. It allows us to deliver truly personalized services quickly, securely, and at scale."
Karen Kim
CEO @Human Managed
Dive deeper into authorization resources


Cerbos Synapse
Authorization decisions are only as good as the data behind them
Enrich every request with identity, resource, and relationship context from your existing systems. No middleware to build, no custom adapters to maintain. Adopt incrementally with zero application code changes.