
Implement authorization once
Replace complicated authorization logic with a single API call and allow product owners and security teams to manage access without touching code.

Implement once, enforce everywhere
Replace scattered if/else permission blocks with a single Cerbos SDK call. Define access in policy, enforce it across every app, API, and AI agent - without reimplementing logic per service.

Plugs into your existing stack
Native SDKs for Go, Node, Python, Java, .NET, Rust, PHP, and Ruby and more. Integrates with your identity provider, API gateway, and CI/CD pipeline. No new infrastructure to learn.

Offload policy management
Let product owners and security teams manage roles, permissions, and tenant rules through Cerbos. You implement authorization once - they handle ongoing changes without touching code.
“What caught our attention was the deployment modes of Cerbos, which were very adherent to our new infrastructure running Kubernetes. We could choose to run as a server or as a sidecar. And it was focused on performance and easier to integrate than other solutions out there because Cerbos uses JSON or YAML; you choose.”
Paulo Henrique Pereira Cardoso, Tech Manager

Implement once, enforce everywhere
Replace scattered if/else permission blocks with a single Cerbos SDK call. Define access in policy, enforce it across every app, API, and AI agent - without reimplementing logic per service.
Plugs into your existing stack
Native SDKs for Go, Node, Python, Java, .NET, Rust, PHP, and Ruby and more. Integrates with your identity provider, API gateway, and CI/CD pipeline. No new infrastructure to learn.
Offload policy management
Let product owners and security teams manage roles, permissions, and tenant rules through Cerbos. You implement authorization once - they handle ongoing changes without touching code.
“What caught our attention was the deployment modes of Cerbos, which were very adherent to our new infrastructure running Kubernetes. We could choose to run as a server or as a sidecar. And it was focused on performance and easier to integrate than other solutions out there because Cerbos uses JSON or YAML; you choose.”
Paulo Henrique Pereira Cardoso, Tech Manager

Update access logic without engineering sprints
Product owners update roles, permissions, and tenant-specific rules through Cerbos - no code deploys, no waiting on engineering.
Support any access model your customers need
RBAC, ABAC, PBAC, multi-tenancy, custom roles - meet enterprise buyer requirements without building from scratch.
Unblock your roadmap from IAM bottlenecks
Stop losing sprints to authorization rework. Cerbos externalizes access control from product code so your team stays focused on what matters.
“Having the separation of the permissions from the code base just makes the code base more elegant. It means they're not tied to specific endpoints. And ultimately it means that different business owners have the ability to actually make updates.”
Henry Arnold, CTO & Co-Founder, Nook

Ship policy changes through your CI/CD
Deploy authorization updates through your existing Git and CI/CD workflow. No manual steps, no separate deployment pipeline.

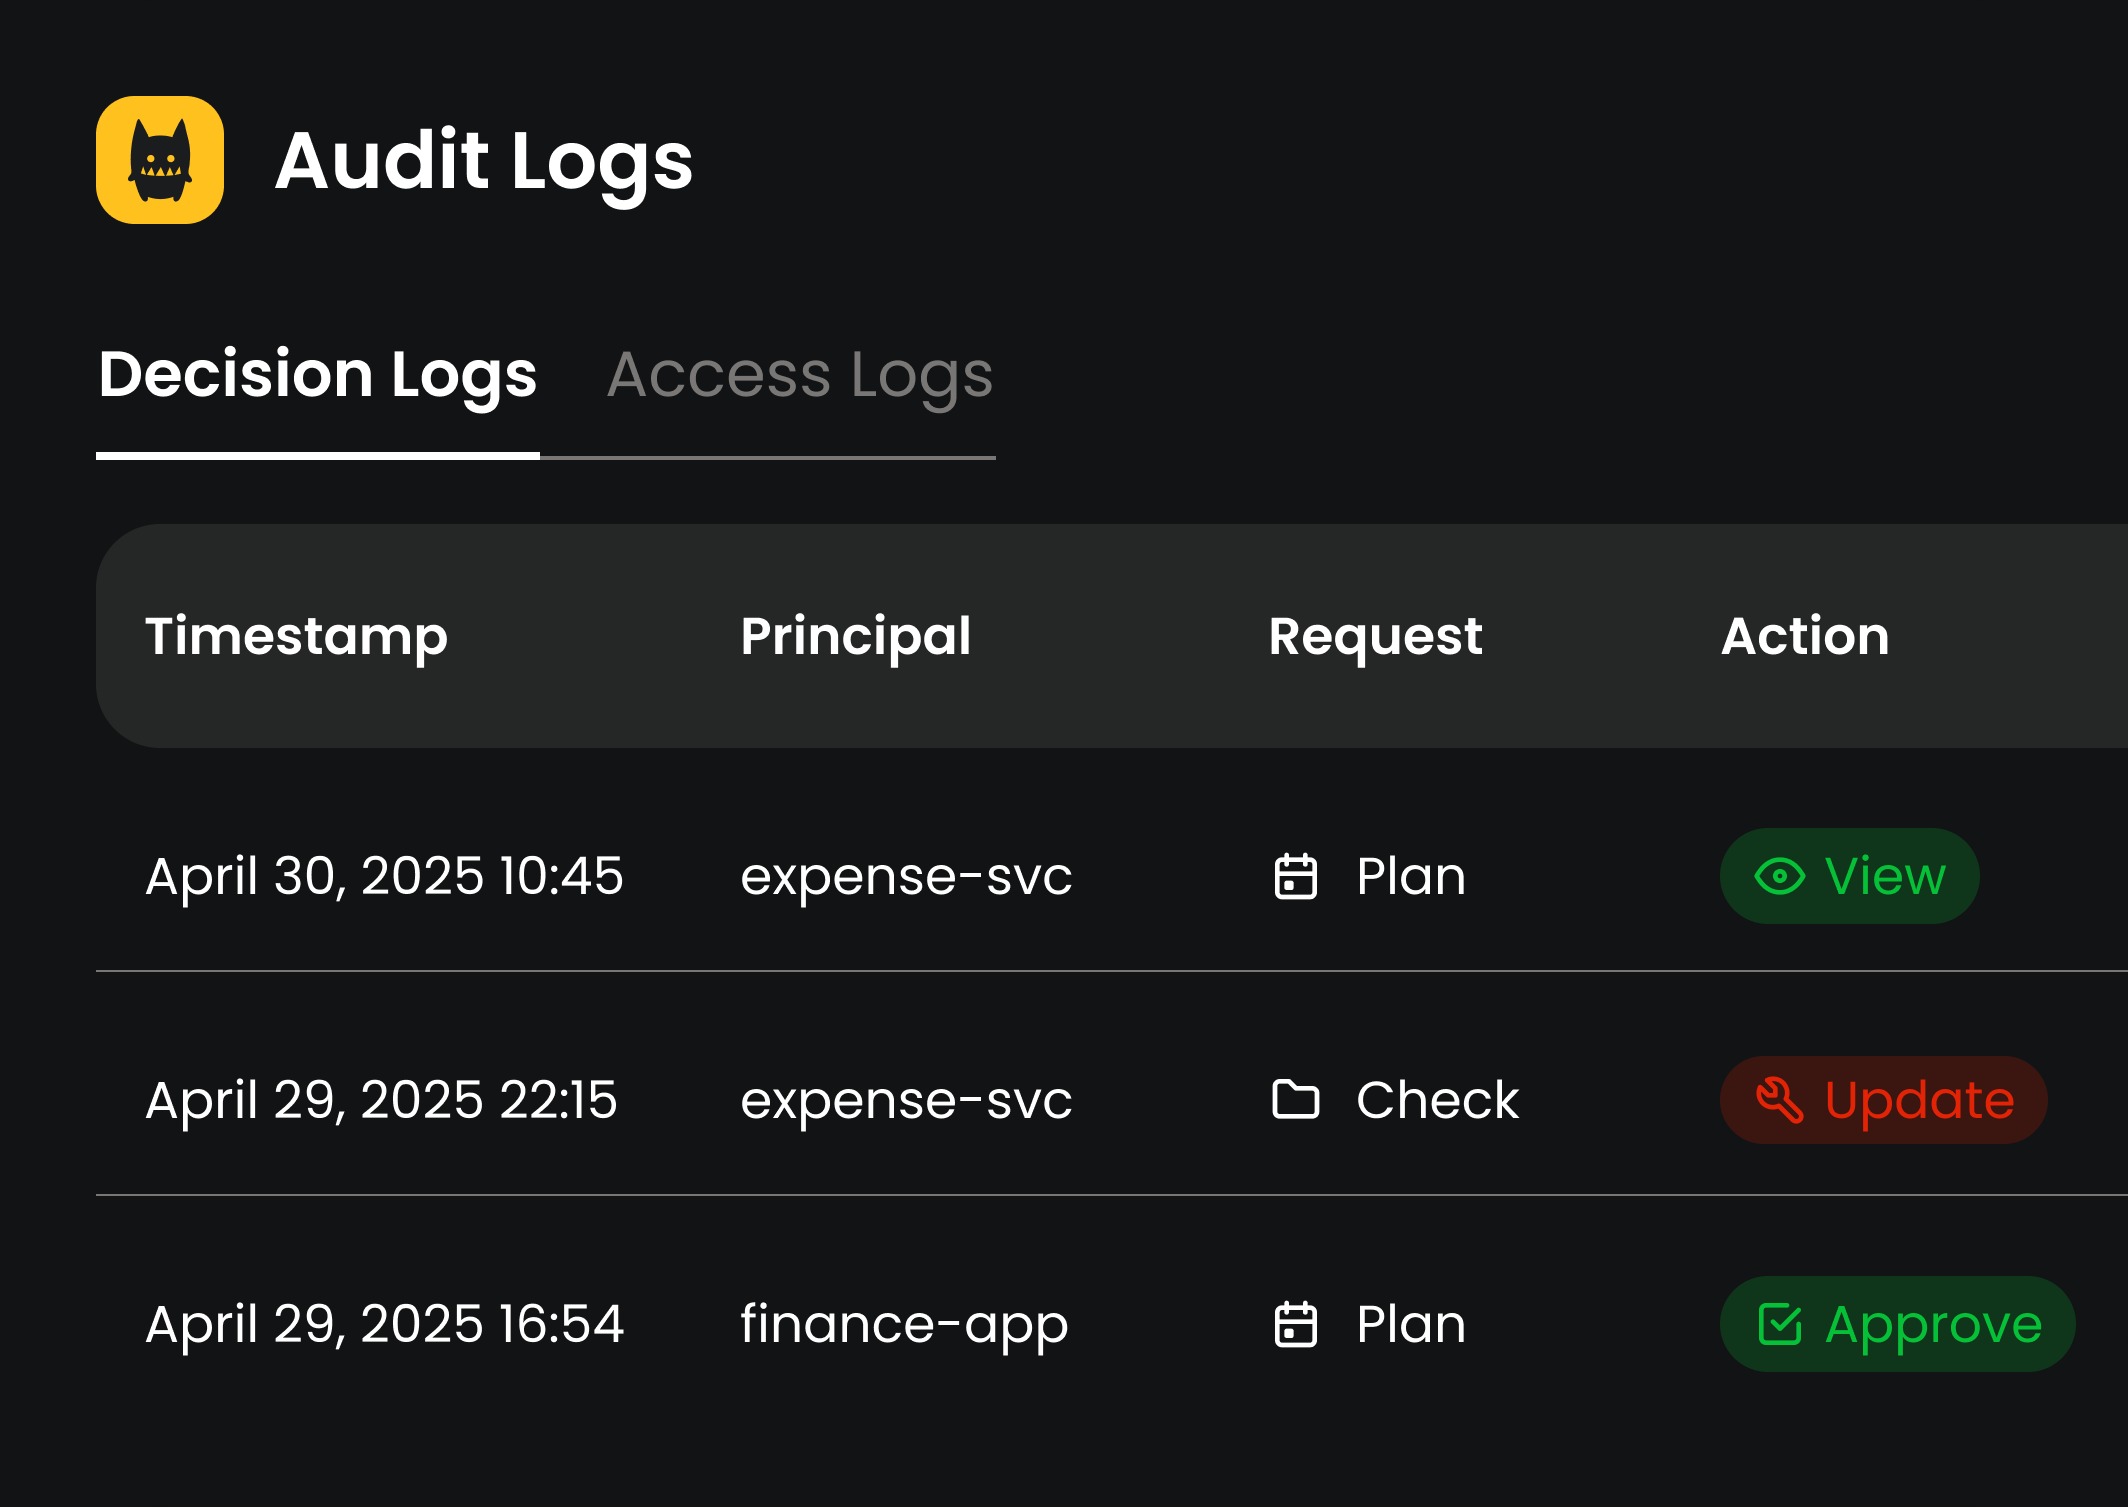
Full visibility into every access decision
Log requests, actions, resources, and authorization decisions across all services - human and machine.

Stay audit-ready without the fire drill
Centralized, structured logs simplify compliance cycles for SOC 2, ISO 27001, HIPAA, PCI DSS, and GDPR.
“One of our favorite features is the audit logs because they allow us to understand what's happening inside the black box. This level of visibility gives us confidence in our security posture.”
Rob Crowe, Principal Engineer



How in-house authorization becomes your bottleneck
Whether you built it from scratch or it's buried in your application code, the result is the same: scattered logic, constant rewrites, and compliance work that never ends - all for a problem that's already been solved.
You're reimplementing the same logic everywhere
Authorization checks scattered across microservices, APIs, and frontend layers. Every new surface means duplicating logic, diverging behavior, and debugging inconsistencies across services.
Every change means touching code
New tenant? New role? New feature flag? Each one requires code changes, engineering review, and a full redeployment - for what should be a configuration update.
You're responsible for auditing and compliance
Hardcoded authorization means you also own the audit trail. Building logging, evidence collection, and compliance reporting from scratch - on top of the authorization logic itself.

Your authorization headache solved
Cerbos externalizes and centralizes authorization

Define your policies
Replace the spaghetti if/else case/switch code with a single function call.

Programmatic policy management
Create, update and manage policies using the Cerbos CLI or via API from your applications.

Flexible policy delivery
Deliver policies from from your existing Git provider, any CI/CD pipeline or directly from the Cerbos Hub interface.

Validate policy changes automatically
Run automated tests in Cerbos Hub's CI pipeline before deploying to your Policy Decision Points.
How Complex centralized scattered roles and permissions with Cerbos.
Consistency across services
Permissions managed from one place
Faster app iterations
“It used to be that somebody on the product team goes to change something, and we forgot to change it in 9 of 10 places. So it was always a disaster. With Cerbos, we have one repo of policies. That's all you have to worry about.”
Steve High
Staff Engineer, Complex
Cerbos authorization in action
End-to-end authorization across applications, infrastructure, and AI systems with a unified policy engine, data layer, and control plane.
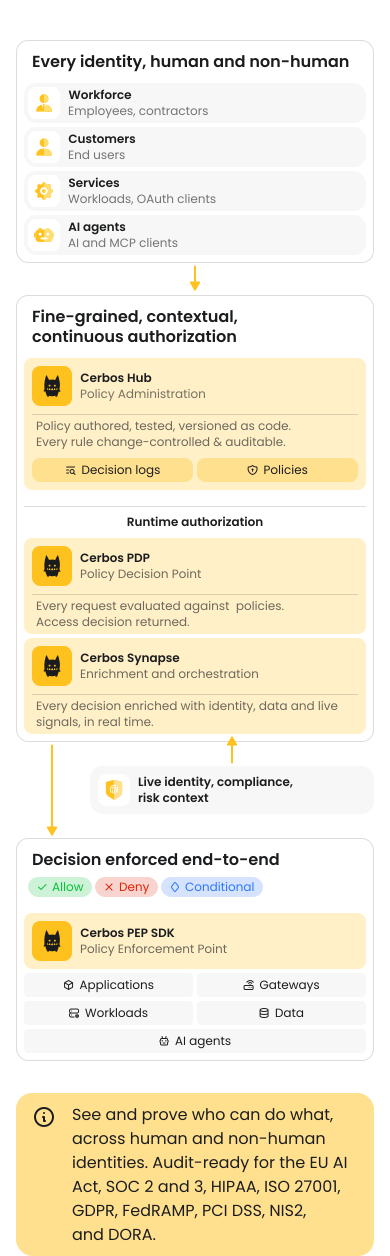
End-to-end authorization platform
Policy management, data enrichment, access decisions, and enforcement in one solution
Authorization management
Cerbos Hub
Policy Administration Point
Cerbos Hub is the control plane for policy authoring, testing, versioning, distribution, and audit visibility. Hub provides end-to-end policy management out of the box.
Data and integration
Cerbos Synapse
Enrichment and Orchestration
Synapse fetches identity, resource, and relationship data from external systems to enrich authorization requests, and translates infrastructure protocols into Cerbos policy checks.
< 1 ms decision time
Cerbos PDP
Policy Decision Point
PDP is an open source authorization engine that evaluates requests against policies and returns access decisions. It's stateless, high-performance, and built to scale horizontally.
Native SDKs
Cerbos PEP SDK
Policy Enforcement Point
Cerbos PEPs are language-native client libraries that connect applications directly to PDPs to enforce real-time access decisions, with SDKs available for all major languages.
Implement authorization once, scale everywhere
Define access in policy, enforce it with one SDK call, and let product and security teams manage changes through Cerbos - without touching your code.
Replace scattered if/else permission blocks with a single Cerbos SDK call. Define access rules in declarative policy, reusable across every service, tenant, and environment. You implement authorization once - Cerbos handles the rest.
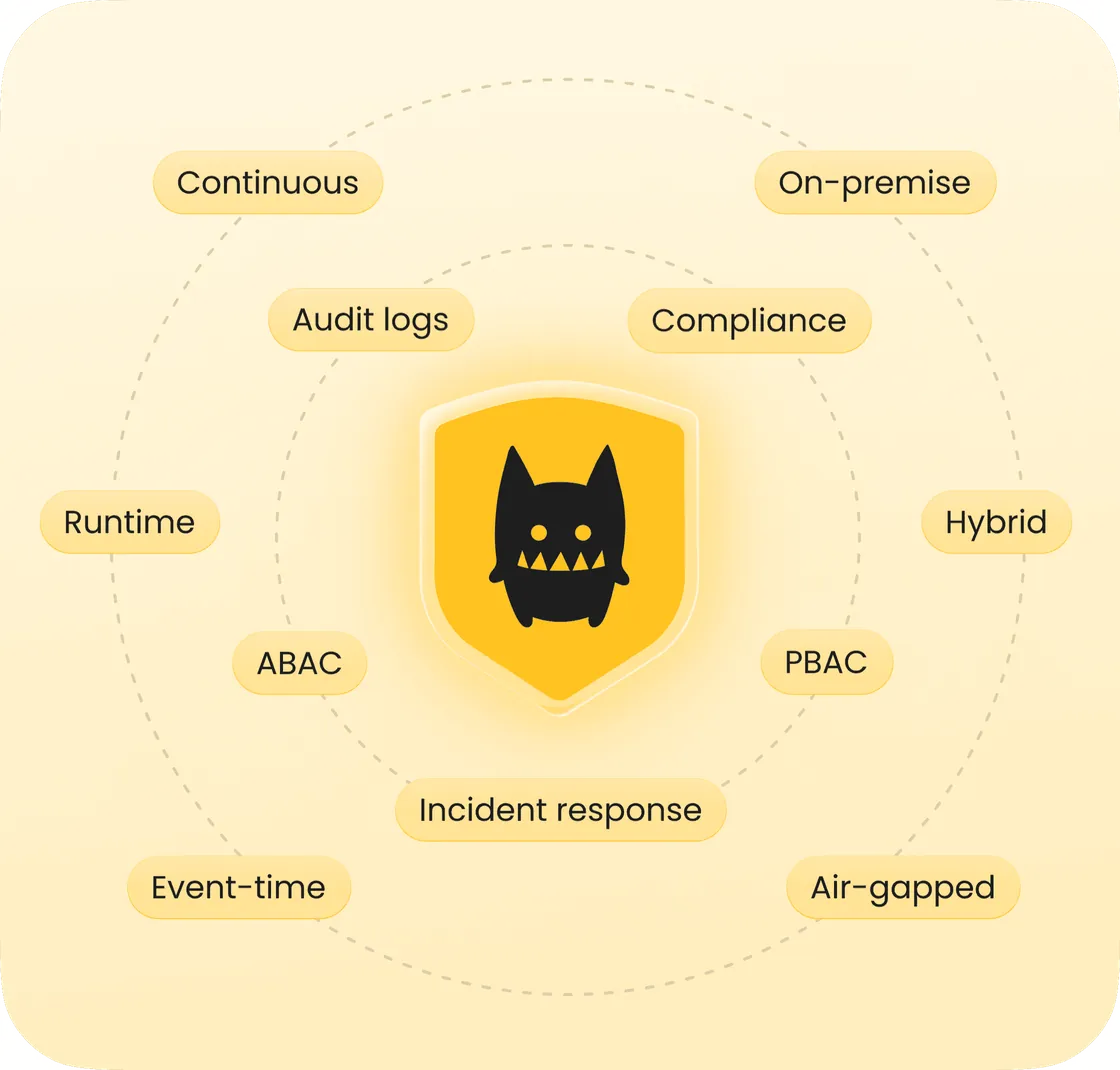
Developer-ready integrations
Works with your existing tools, workflows, and infrastructure
Flexible policy sources
Add policies from any Git provider, any CI/CD tool, Cerbos Hub API, cerbosctl CLI, direct UI upload.



SDKs and integration for every stack
Use SDKs for JS, Go, Python, Java, .NET, Rust, PHP, and Ruby, plus integrations for AI frameworks, vector databases, and MCP servers.





Deployment targets
Deploy to Cerbos PDPs in containers, serverless, edge, or multi-region clusters.


Compliance ready audit logs
Ensure Zero Trust, compliance and audit readiness for FedRAMP, SOC 2, SOC 3, ISO 27001, HIPAA, PCI DSS, and GDPR.


Access control for every use case
AI systems authorization


Enterprise software authorization


Authorization software that scales with your business
ABAC
RBAC
ReBAC
PBAC
Runtime
Event-time
Admin-time
Audit-time
Cloud
Self-hosted
On-premise
Air-gapped
Non-human identities
Human identities
Workloads

Contextual, continuous authorization
Fine grained, contextual, continuous authorization at scale
Why engineering teams love Cerbos
Why teams love Cerbos
"When I did an audit, I found that the cost of managing authorization and authentication in-house over the entire lifespan of the company was in the 7 figures. Cerbos saved that. Deploying Cerbos has allowed our engineers to spend their time on what really matters for our success."
Chuck Hardy
Head of Engineering @Salesroom
"Having to modify authorization is a five-minute job now. Having to troubleshoot authorization is a five-minute job. So that has actually allowed the team to spend more time where it really matters on the platform."
Karen Kim
CEO @Human Managed
"We rely on Cerbos to make authorization decisions across the whole mesh - millions of times a day. And it’s fast. We don’t even think about it anymore. It just works."

Rob Crowe
Principal Engineer @Utility Warehouse
"We went from one user - every role, to a world where there are many users - many roles. And the product, it relies on Cerbos to actually bring the value that we want to bring to customers. All of our customers are relying on Cerbos, by relying on the product, which is of course relying on Cerbos."
Joe Lines
CEO & Co-Founder @Nook
"One of our big considerations was speed. We have strict latency tolerances. When it comes to Cerbos - you can call it a hundred times during a request and it doesn't matter. It's incredibly fast."
Steve High
Staff Engineer @Complex
"The main reason we switched to Cerbos was to have a sophisticated authorization software to help organize and handle our authorization. We wanted to focus on domain related features and spend less time backtracking and fixing issues with our authorization."
Lead Software Developer at @BarrierSystems
"Cerbos enables us to go to market very quickly, compared to an in-house solution. It allows us to offer new products faster, because creating or editing policies is so easy."
Engin Attar
Head of Product and Growth, Co-Founder @Debite
"We got the foundation set. Now we can scale and include more complex policies. And we can grow in the right direction and with the right security thanks to Cerbos authorization management."
Edgar Rivera
CTO @4gcapital
"Having the separation of the permissions from the code base just makes the code base more elegant. It makes the permissioning more elegant. It means they're centralized, so they're not tied to specific endpoints. And ultimately it means that different business owners have the ability to actually make updates."
Henry Arnold
CTO & Co-Founder @Nook
"We're not worried about scaling because we can easily increase our load on Cerbos. It will also be easy for us to change how we're distributing policies as we reach different points of scale."
David Workman
Senior Software Engineer @ Salesroom

"Offering dynamic roles and permissions makes us more competitive in the market. We’re providing companies with a software that can be adapted to their workflows."
Ibrahim Bou Ncoula
CTO @Supy
"We can create unlimited conditions, attributes, and parameters at any level of granularity without writing any code. It allows us to deliver truly personalized services quickly, securely, and at scale."
Karen Kim
CEO @Human Managed
"When I did an audit, I found that the cost of managing authorization and authentication in-house over the entire lifespan of the company was in the 7 figures. Cerbos saved that. Deploying Cerbos has allowed our engineers to spend their time on what really matters for our success."
Chuck Hardy
Head of Engineering @Salesroom
"Having to modify authorization is a five-minute job now. Having to troubleshoot authorization is a five-minute job. So that has actually allowed the team to spend more time where it really matters on the platform."
Karen Kim
CEO @Human Managed
"We rely on Cerbos to make authorization decisions across the whole mesh - millions of times a day. And it’s fast. We don’t even think about it anymore. It just works."
Rob Crowe
Principal Engineer @Utility Warehouse
"We went from one user - every role, to a world where there are many users - many roles. And the product, it relies on Cerbos to actually bring the value that we want to bring to customers. All of our customers are relying on Cerbos, by relying on the product, which is of course relying on Cerbos."
Joe Lines
CEO & Co-Founder @Nook
"One of our big considerations was speed. We have strict latency tolerances. When it comes to Cerbos - you can call it a hundred times during a request and it doesn't matter. It's incredibly fast."
Steve High
Staff Engineer @Complex
"The main reason we switched to Cerbos was to have a sophisticated authorization software to help organize and handle our authorization. We wanted to focus on domain related features and spend less time backtracking and fixing issues with our authorization."
Lead Software Developer at @BarrierSystems
"Cerbos enables us to go to market very quickly, compared to an in-house solution. It allows us to offer new products faster, because creating or editing policies is so easy."
Engin Attar
Head of Product and Growth, Co-Founder @Debite
"We got the foundation set. Now we can scale and include more complex policies. And we can grow in the right direction and with the right security thanks to Cerbos authorization management."
Edgar Rivera
CTO @4gcapital
"Having the separation of the permissions from the code base just makes the code base more elegant. It makes the permissioning more elegant. It means they're centralized, so they're not tied to specific endpoints. And ultimately it means that different business owners have the ability to actually make updates."
Henry Arnold
CTO & Co-Founder @Nook
"We're not worried about scaling because we can easily increase our load on Cerbos. It will also be easy for us to change how we're distributing policies as we reach different points of scale."
David Workman
Senior Software Engineer @ Salesroom
"Offering dynamic roles and permissions makes us more competitive in the market. We’re providing companies with a software that can be adapted to their workflows."
Ibrahim Bou Ncoula
CTO @Supy
"We can create unlimited conditions, attributes, and parameters at any level of granularity without writing any code. It allows us to deliver truly personalized services quickly, securely, and at scale."
Karen Kim
CEO @Human Managed
Resources: from quickstart to production

Ready to solve your authorization headache?
See how Cerbos replaces scattered permissions logic with a single API call, and lets you hand off policy management for good.