Tech blog
Demos, implementation guides, product updates and broader takes on authorization, identity and security.
Agent skill for writing authorization policies in AWS Kiro
AWS Kiro is spec-driven, which means the access model is captured properly before any YAML gets written. This guide walks through installing the Cerbos policy skill in Kiro, the spec-then-policy workflow, how the skill picks up AWS Cognito attributes, and how validation runs against the real Cerbos compiler.
5 factors to weigh when building authorization architecture
A product-creation journey always requires new thinking about a permissions strategy. Learn about the 5 instances when your authorization logic needs to be analyzed, evolved, changed and monitored, as your software product evolves.
Fine grained access control: What it actually takes to get it right
Fine grained access control lets you authorize based on user attributes, resource ownership, and context instead of broad roles. This guide covers RBAC, ABAC, ReBAC, PBAC models, embedded vs. externalized authorization, real policy examples, and practical implementation patterns for engineering teams.
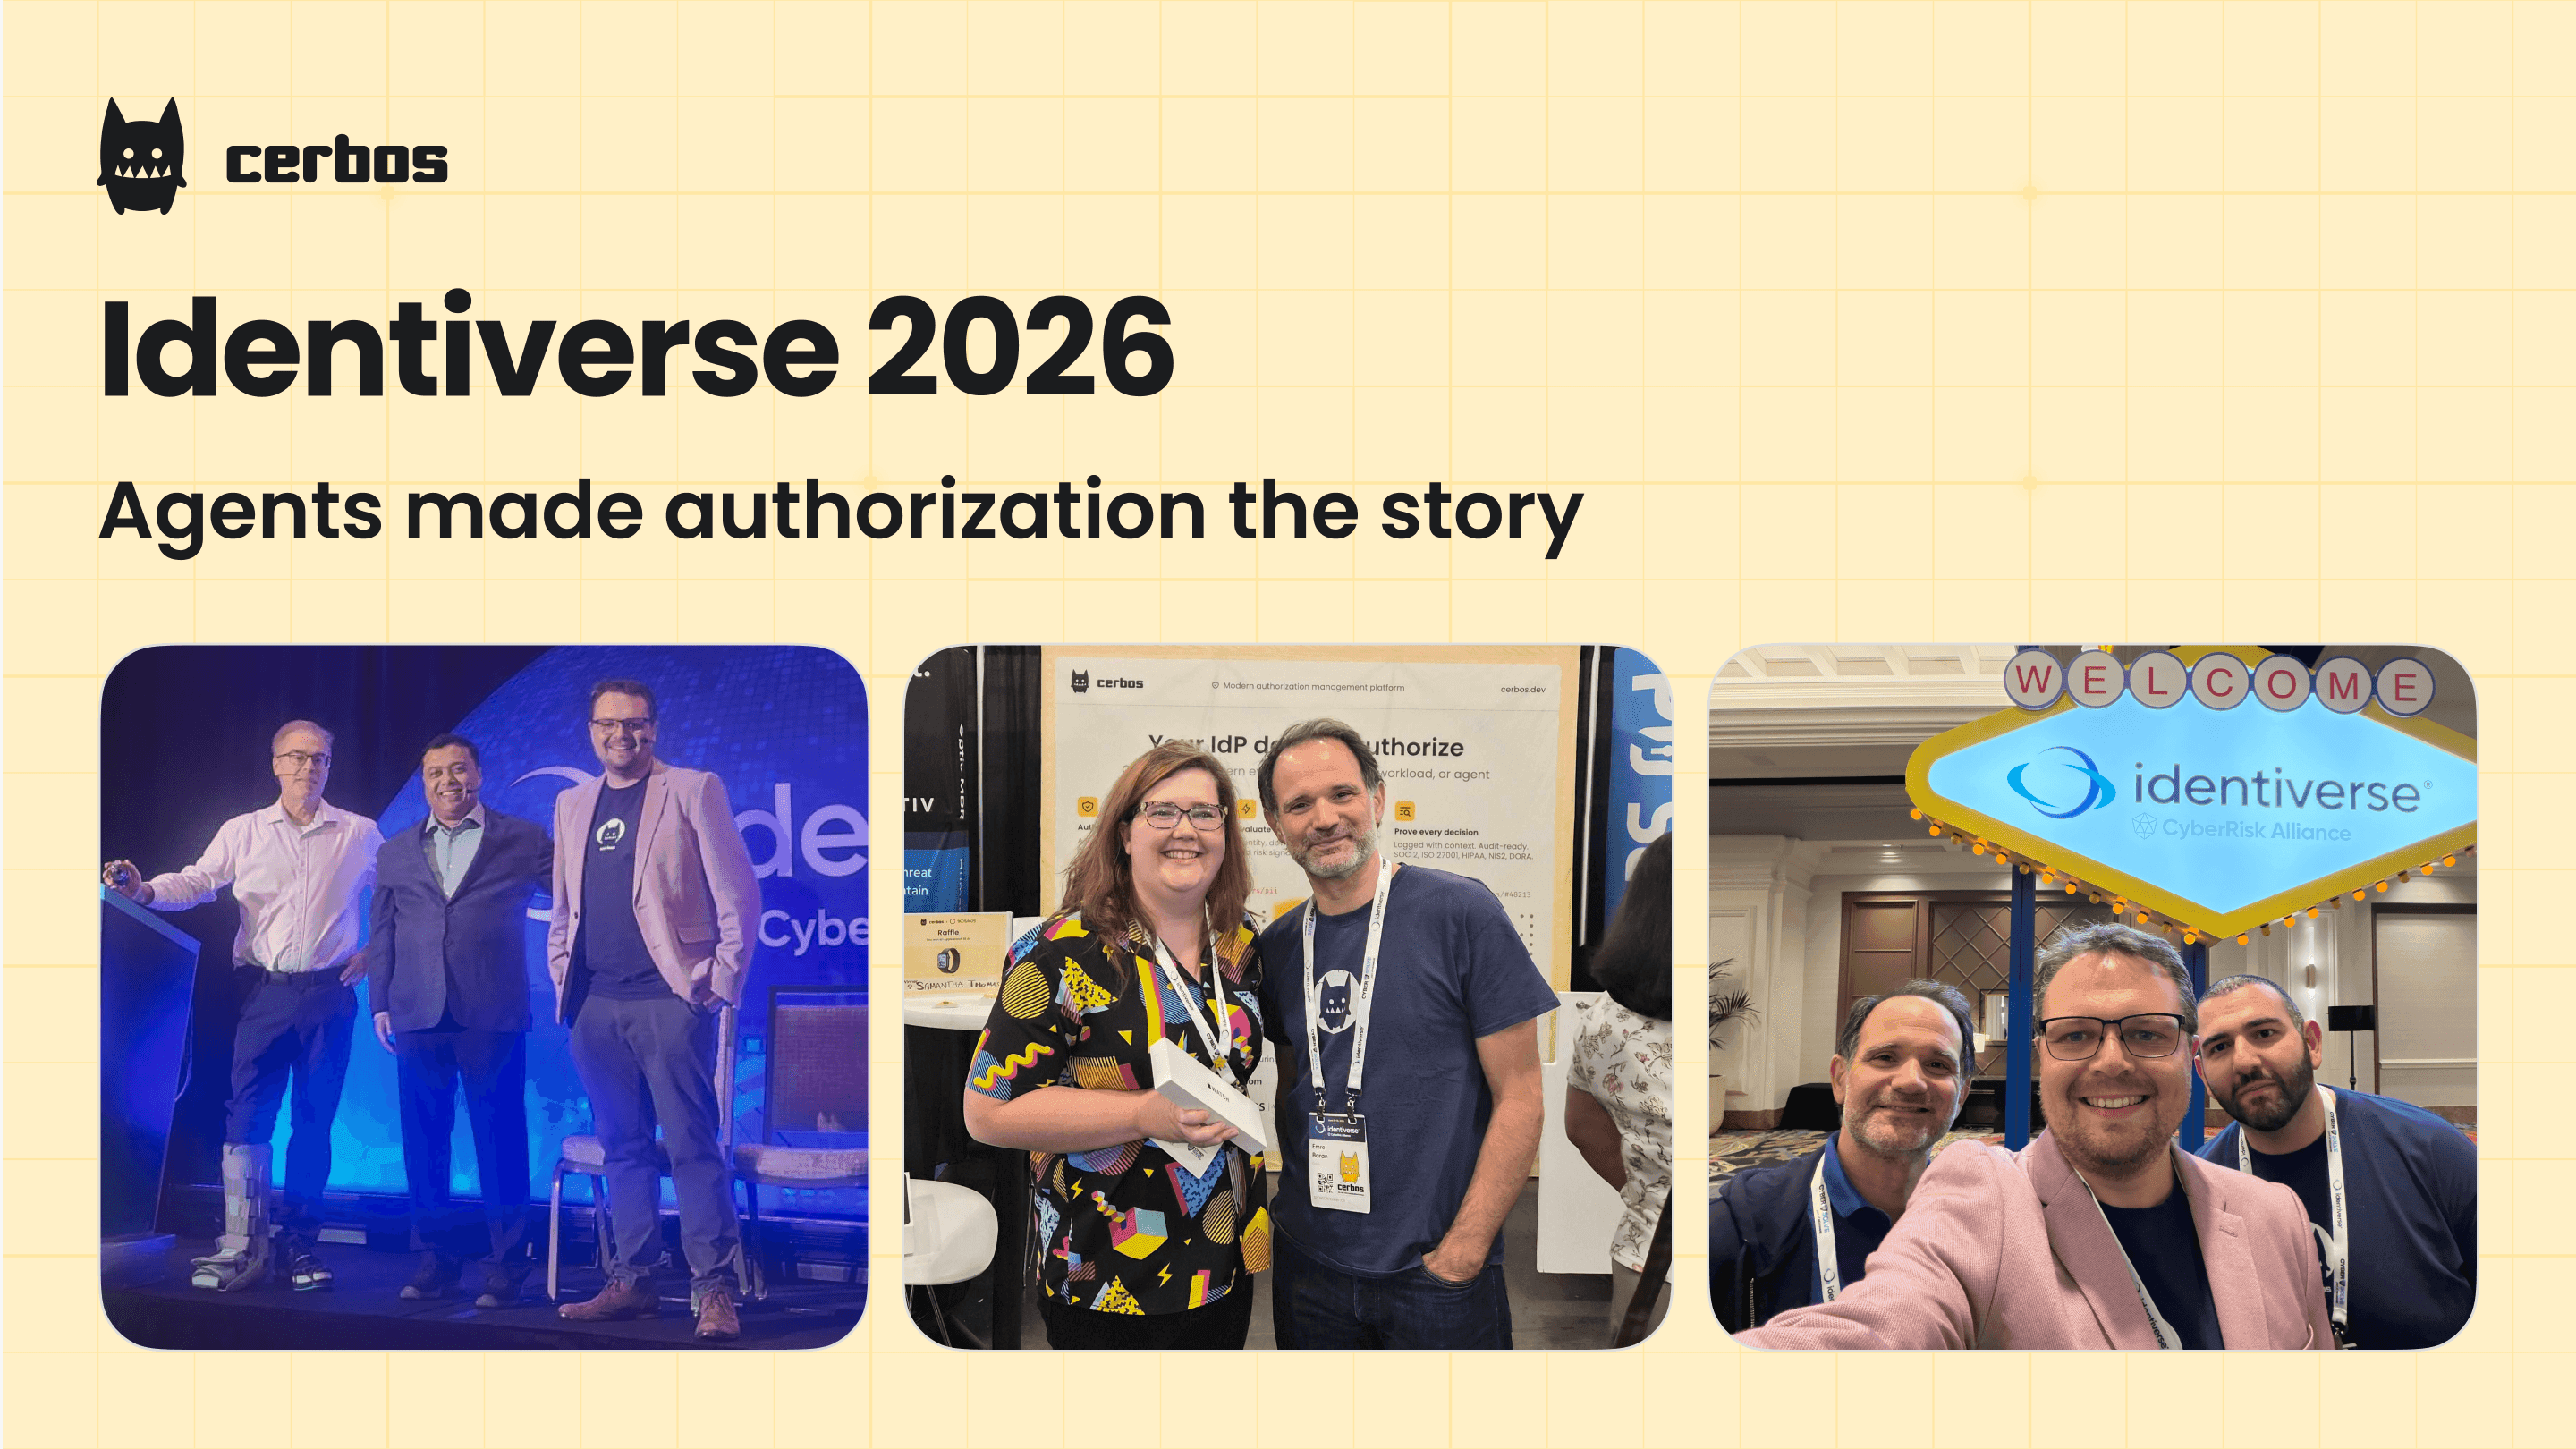
Identiverse 2026: Agents made authorization the story
Takeaways from Identiverse 2026, where AI agents pushed authorization to the front. Delegated authorization, the Shared Signals Framework, AuthZEN agent authorization, and why prompts aren't controls. Notes from three AuthZEN sessions and the best talks of the week.

Authentication vs Authorization
Authentication vs authorization explained. AuthN verifies who a user is, AuthZ decides what they can do. This guide covers ID and access tokens, OAuth 2.0, OpenID Connect, SAML, SSO, RBAC and ABAC, the key differences between the two, and the mistakes teams make building them.
Agent skill for building Cerbos Synapse extensions
A new agent skill that builds Cerbos Synapse extensions for you. Describe what you want to enrich, map, or expose, and it picks the extension kind and runtime, scaffolds the files, wires config, and runs it against a local PDP. Covers CEL, Starlark, and WASM in Go, TypeScript, or Python.
Keycloak vs ZITADEL for self hosted IAM
Compare Keycloak and ZITADEL for self hosted IAM. See SSO, MFA, federation, multi-tenancy, operations, authorization limits, and Cerbos fit.
Mapping business requirements to authorization policy for e-commerce
A practical walkthrough of how e-commerce business rules become authorization policy. Covers customer data access, vendor product management, and order lifecycle control using RBAC, ABAC, and PBAC in Cerbos. Includes derived roles, attribute conditions, time-based rules, and a built-in test framework to verify each policy before production.
How to secure microservices without creating a distributed nightmare
How to secure microservices across five critical layers, from authentication and token propagation to authorization, API gateways, and Zero Trust. Covers common vulnerabilities during monolith-to-microservices migration, how Netflix secured their architecture, and how to enforce consistent access control across distributed services.
Governing AI agents at the gateway with Cerbos and agentgateway
How to govern AI agents at the gateway with agentgateway and Cerbos. This covers the three authorization questions on every agent hop, which model an identity can call, which MCP servers and tools it can open, and what a tool call is actually asking for, all from one policy bundle over Envoy ext_authz.
How to secure AI agents and MCP tools at the gateway with LiteLLM and Cerbos
Add policy-based authorization to a LiteLLM AI gateway with Cerbos. Control which models each user or agent can call, hide tools the caller shouldn't see, and bind MCP tool arguments to caller attributes, all enforced at the proxy with no application changes.
Introducing Cerbos Hub Insights: A live view of what your authorization layer is doing
Cerbos Hub Insights aggregates the decisions your PDPs make into charts and rankings, so patterns like a spike in denials become obvious without scrolling the audit log. Track allows, denies, and active principals over time, built entirely from audit data you already send to Cerbos Hub.
Recommended content
Mapping business requirements to authorization policy

eBook: Zero Trust for AI, securing MCP servers
Experiment, learn, and prototype with Cerbos Playground

eBook: How to adopt externalized authorization

Framework for evaluating authorization providers and solutions