Authorization management platform
Authorize every identity. Govern every action.
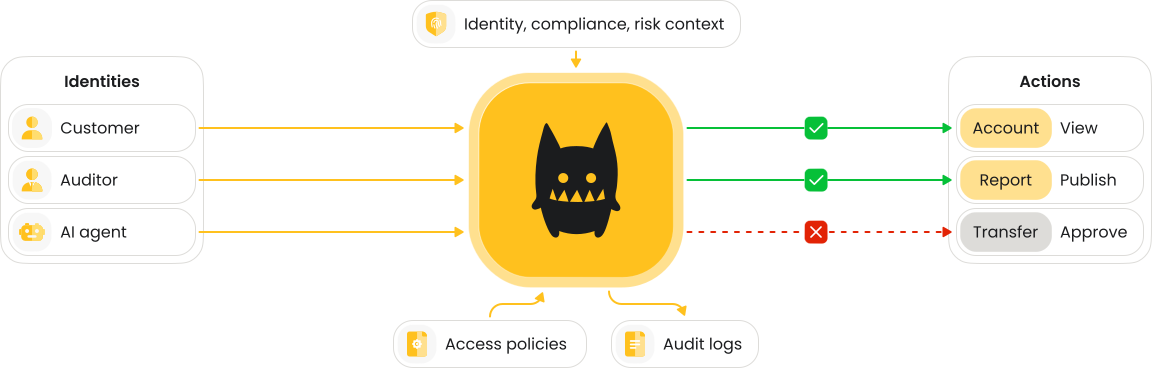
Enforce fine-grained, contextual, and continuous authorization across applications, gateways, workloads, and AI agents.

See and govern every access decision
Gain full visibility into what every identity can access. No more scattered authorization logic creating blind spots.

Control AI agent access
Define AI agent and MCP boundaries before they go live. Revoke access in seconds through policy. Always know exactly what every agent can access.

Prove compliance at any time
Get instant logs for every decision: who, what, when, which policy. Audit-ready for SOC 2, ISO 27001, HIPAA, GDPR, NIS2, DORA, FedRAMP.


Control authorization logic in one place
Define, approve, and update policies centrally. Replace scattered if-statements with a single function call.

Ship authorization in one sprint
Deploy roles and permissions without code changes. RBAC, ABAC, ReBAC, PBAC supported out of the box.

Scale with your architecture
Handle millions of authorization decisions per second across distributed systems and AI agents. Stateless. Deploy in cloud, on-prem, or air-gapped.

Close the gap in your IAM stack
Your IdP authenticates. Your IGA provisions roles. Cerbos controls what identities actually do at the resource level, at runtime.
Govern every identity type
Manage access across your entire identity fabric in one place. Centralized policies for users, service accounts, NHIs, and AI agents.

Secure AI agents with guardrails
Define what each AI agent can access before it goes live - and revoke that access in seconds through policy if anything changes.





Authorization was always the gap. AI is making it impossible to ignore.

Over-permissioned access
AI agents and services can do more than they should. One mistake can expose sensitive data or trigger unauthorized actions.

AI agents blur identity lines
AI agents act on behalf of users through MCP clients and other interfaces, masking who initiated the action. When the system can’t tell them apart, agents inherit permissions they should never have.

Standing access never expires
Long-lived tokens and shared credentials stay valid long after they are needed, increasing the chance of compromise.

No fine-grained kill switch
If an agent goes beyond its scope, access continues until someone rotates credentials or restarts systems. No way to revoke a single action in seconds.

Access control for every use case
Single authorization management platform for every identity, every decision, at every layer.

AI systems
authorization
AI systems authorization


Enterprise software
authorization
Enterprise software authorization


Authorization software that scales with your business

ABAC
RBAC
ReBAC
PBAC
Runtime
Event-time
Admin-time
Audit-time
Cloud
Self-hosted
On-premise
Air-gapped
Non-human identities
Human identities
Workloads
Authorization loved by engineers and leadership
"We can trace every permission, investigate suspicious behavior, and answer questions about who did what, when, and why. We’ve gone from guesswork to forensic-level auditing across humans, machines, and everything in between."
Rob Crowe, Principal Engineer


Time to market
100x faster launch
Deploy new roles and permissions instantly for RBAC, ABAC, ReBAC, PBAC.

Security
Enable AI adoption safely
Define what every AI agent can do and access. Revoke permissions in seconds.

ROI
Skip the 12 months build time
Eliminate the need to design, operate, and evolve authorization in-house.

Compliance
Audit-ready logs
Log every allow/deny decision with fine-grained context. Full traceability across all identities.
Why Cerbos? To control what happens after login.
Your IdP authenticates. Your IGA provisions roles. Cerbos controls what identities are allowed to do, at the moment decisions are enforced.
See how Cerbos works for your team

Identity teams
Get fine-grained visibility and control over what every user, service, and AI agent can do.

Security teams
Stay secure and audit-ready as AI enters production.

Product teams
Ship faster without authorization holding you back.

Developers
Implement authorization once, let product and security teams handle the rest.

Runtime authorization for Zero Trust
Be compliance-ready with every access decision, human or AI


SOC 2

SOC 3
HIPAA

ISO 27001

GDPR

FedRAMP

PCI DSS

NIS2

DORA
SOC 2
SOC 3
HIPAA
ISO 27001
GDPR
FedRAMP
PCI DSS
NIS2
DORA

Capture every decision for all identities
Log requests, actions, resources, access outcomes, and service-to-service authorization calls for both humans and machines.

Trace policy lineage
See the exact policy, version, and release behind each decision for complete traceability.

Monitor with context
Review detailed logs, policy versions, and real-time metrics across all PDPs and environments.

Simplify audits and compliance
Maintain centralized, structured logs on-premise to support audits and demonstrate readiness for FedRAMP, SOC 2&3, ISO 27001, HIPAA, PCI DSS, and GDPR.


Cerbos plugs into your existing stack
Works with your existing tools, workflows, and infrastructure

Data and infrastructure
Enforce authorization across API gateways, data platforms, and infrastructure services.




AI infrastructure
Integrate fine grained policy based access control around AI systems.


SDKs
Use Cerbos SDKs for languages like JS, Python, Go, Rust, Java, and .NET to authorize requests from your application code.




IdPs
Connect to your existing identity providers for seamless authentication context.


End-to-end authorization platform
Policy management, data enrichment, access decisions, and enforcement in one solution
Authorization management
Cerbos Hub
Policy Administration Point
Cerbos Hub is the control plane for policy authoring, testing, versioning, distribution, and audit visibility. Hub provides end-to-end policy management out of the box.
Data and integration
Cerbos Synapse
Enrichment and Orchestration
Synapse fetches identity, resource, and relationship data from external systems to enrich authorization requests, and translates infrastructure protocols into Cerbos policy checks.
< 1 ms decision time
Cerbos PDP
Policy Decision Point
PDP is an open source authorization engine that evaluates requests against policies and returns access decisions. It's stateless, high-performance, and built to scale horizontally.
Native SDKs
Cerbos PEP SDK
Policy Enforcement Point
Cerbos PEPs are language-native client libraries that connect applications directly to PDPs to enforce real-time access decisions, with SDKs available for all major languages.

Recognized by the community
Award-winning technology, built for security and scale
With a strong open source foundation, AuthZEN compliance, and multiple industry awards, Cerbos has been recognized as a secure and reliable authorization software since 2021. Our CPO Alex Olivier co-chairs the OpenID AuthZEN working group.

Hackernoon Startup Awards 2025
Startups 100 Index 2025

API World 2025 Awards

Intellyx Digital Innovator 2023
Integrations with industry leading technologies



Fine-grained identity security
Why teams choose Cerbos
"When I did an audit, I found that the cost of managing authorization and authentication in-house over the entire lifespan of the company was in the 7 figures. Cerbos saved that. Deploying Cerbos has allowed our engineers to spend their time on what really matters for our success."
Chuck Hardy
Head of Engineering @Salesroom
"Having to modify authorization is a five-minute job now. Having to troubleshoot authorization is a five-minute job. So that has actually allowed the team to spend more time where it really matters on the platform."
Karen Kim
CEO @Human Managed
"We rely on Cerbos to make authorization decisions across the whole mesh - millions of times a day. And it’s fast. We don’t even think about it anymore. It just works."

Rob Crowe
Principal Engineer @Utility Warehouse
"We went from one user - every role, to a world where there are many users - many roles. And the product, it relies on Cerbos to actually bring the value that we want to bring to customers. All of our customers are relying on Cerbos, by relying on the product, which is of course relying on Cerbos."
Joe Lines
CEO & Co-Founder @Nook
"One of our big considerations was speed. We have strict latency tolerances. When it comes to Cerbos - you can call it a hundred times during a request and it doesn't matter. It's incredibly fast."
Steve High
Staff Engineer @Complex
"The main reason we switched to Cerbos was to have a sophisticated authorization software to help organize and handle our authorization. We wanted to focus on domain related features and spend less time backtracking and fixing issues with our authorization."
Lead Software Developer at @BarrierSystems
"Cerbos enables us to go to market very quickly, compared to an in-house solution. It allows us to offer new products faster, because creating or editing policies is so easy."
Engin Attar
Head of Product and Growth, Co-Founder @Debite
"We got the foundation set. Now we can scale and include more complex policies. And we can grow in the right direction and with the right security thanks to Cerbos authorization management."
Edgar Rivera
CTO @4gcapital
"Having the separation of the permissions from the code base just makes the code base more elegant. It makes the permissioning more elegant. It means they're centralized, so they're not tied to specific endpoints. And ultimately it means that different business owners have the ability to actually make updates."
Henry Arnold
CTO & Co-Founder @Nook
"We're not worried about scaling because we can easily increase our load on Cerbos. It will also be easy for us to change how we're distributing policies as we reach different points of scale."
David Workman
Senior Software Engineer @ Salesroom

"Offering dynamic roles and permissions makes us more competitive in the market. We’re providing companies with a software that can be adapted to their workflows."
Ibrahim Bou Ncoula
CTO @Supy
"We can create unlimited conditions, attributes, and parameters at any level of granularity without writing any code. It allows us to deliver truly personalized services quickly, securely, and at scale."
Karen Kim
CEO @Human Managed
"When I did an audit, I found that the cost of managing authorization and authentication in-house over the entire lifespan of the company was in the 7 figures. Cerbos saved that. Deploying Cerbos has allowed our engineers to spend their time on what really matters for our success."
Chuck Hardy
Head of Engineering @Salesroom
"Having to modify authorization is a five-minute job now. Having to troubleshoot authorization is a five-minute job. So that has actually allowed the team to spend more time where it really matters on the platform."
Karen Kim
CEO @Human Managed
"We rely on Cerbos to make authorization decisions across the whole mesh - millions of times a day. And it’s fast. We don’t even think about it anymore. It just works."
Rob Crowe
Principal Engineer @Utility Warehouse
"We went from one user - every role, to a world where there are many users - many roles. And the product, it relies on Cerbos to actually bring the value that we want to bring to customers. All of our customers are relying on Cerbos, by relying on the product, which is of course relying on Cerbos."
Joe Lines
CEO & Co-Founder @Nook
"One of our big considerations was speed. We have strict latency tolerances. When it comes to Cerbos - you can call it a hundred times during a request and it doesn't matter. It's incredibly fast."
Steve High
Staff Engineer @Complex
"The main reason we switched to Cerbos was to have a sophisticated authorization software to help organize and handle our authorization. We wanted to focus on domain related features and spend less time backtracking and fixing issues with our authorization."
Lead Software Developer at @BarrierSystems
"Cerbos enables us to go to market very quickly, compared to an in-house solution. It allows us to offer new products faster, because creating or editing policies is so easy."
Engin Attar
Head of Product and Growth, Co-Founder @Debite
"We got the foundation set. Now we can scale and include more complex policies. And we can grow in the right direction and with the right security thanks to Cerbos authorization management."
Edgar Rivera
CTO @4gcapital
"Having the separation of the permissions from the code base just makes the code base more elegant. It makes the permissioning more elegant. It means they're centralized, so they're not tied to specific endpoints. And ultimately it means that different business owners have the ability to actually make updates."
Henry Arnold
CTO & Co-Founder @Nook
"We're not worried about scaling because we can easily increase our load on Cerbos. It will also be easy for us to change how we're distributing policies as we reach different points of scale."
David Workman
Senior Software Engineer @ Salesroom
"Offering dynamic roles and permissions makes us more competitive in the market. We’re providing companies with a software that can be adapted to their workflows."
Ibrahim Bou Ncoula
CTO @Supy
"We can create unlimited conditions, attributes, and parameters at any level of granularity without writing any code. It allows us to deliver truly personalized services quickly, securely, and at scale."
Karen Kim
CEO @Human Managed
Policy based access control at scale
Purpose built authorization, not a generic policy engine
 Generic policy engines |  Cerbos |
|---|---|
Policy language General-purpose policy languages designed for broader use cases. | Policy language YAML policies purpose-built for authorization, readable by security teams. |
Authorization model Authorization patterns must be assembled from generic primitives. | Authorization model First-class RBAC, ABAC, PBAC, and ReBAC with principal/resource/action semantics. |
Evaluation latency Varies by policy complexity and engine architecture. | Evaluation latency Sub-millisecond, optimized for per-request evaluation at machine speed. |
Policy lifecycle Custom sync, manual distribution, separate CI/CD tooling. | Policy lifecycle Cerbos: managed policy lifecycle with CI/CD, testing, and real-time distribution. |
Audit and compliance Decision logs require additional infrastructure to capture and correlate. | Audit and compliance Structured decision logs with policy version lineage, built in. |
Authorization for enterprise software and AI
Externalized, policy-based, runtime authorization for your apps, enterprise software, AI systems and workflows.